Strategy8 min readPerspective
What if the AI hype is misleading and the business model changes?
How open-weight models and private AI infrastructure could reshape enterprise AI economics and create new opportunities for IT consulting.
Technical Lead Consultant / Solution Architect
I translate EU regulation into working IT architecture: cloud, security and governance for enterprise systems.
I design and deliver Microsoft Dynamics 365, Power Platform and Azure solutions for organisations that must meet EU requirements such as NIS2, GDPR and the EU AI Act. My focus is where architecture decisions, security guardrails and regulatory obligations meet: integration and data migration, application lifecycle management, architecture governance and, more recently, AI readiness.
Typical situations I work on: implementations that need to get back on track, migrations with too much rework, and AI or data initiatives that need an architecture and compliance review before they go live.
Evidence
Compliance, security, platforms and enterprise IT are parts of the same job: building systems that work and can be defended. Each area links to the experience, case studies, projects and articles behind it.
Translating EU requirements (EU AI Act, GDPR, NIS2) into architecture decisions and design reviews.
Security guardrails in delivery: ALM and CI/CD, access control, and privacy and security by design.
Building on and with platforms: Power Platform and Dataverse in client work, and my own SaaS products.
Cloud migrations, integration and application lifecycle management for international enterprise systems.
Experience
Selected work
Anonymised client work, written up as short case studies, and personal projects built in my own time.
Professional · client project (anonymised)
Energy · Netherlands and Germany
Professional · client project (anonymised)
Aviation · Netherlands
Personal project
FreeCVTool · Clinical Conformity · Governance Foundry
Writing
A selection of hands-on implementation guides, regulatory analysis and opinion pieces.Articles about regulation are analysis from an IT architecture perspective, not legal advice.
Strategy8 min readPerspective
How open-weight models and private AI infrastructure could reshape enterprise AI economics and create new opportunities for IT consulting.
Security8 min readImplementation
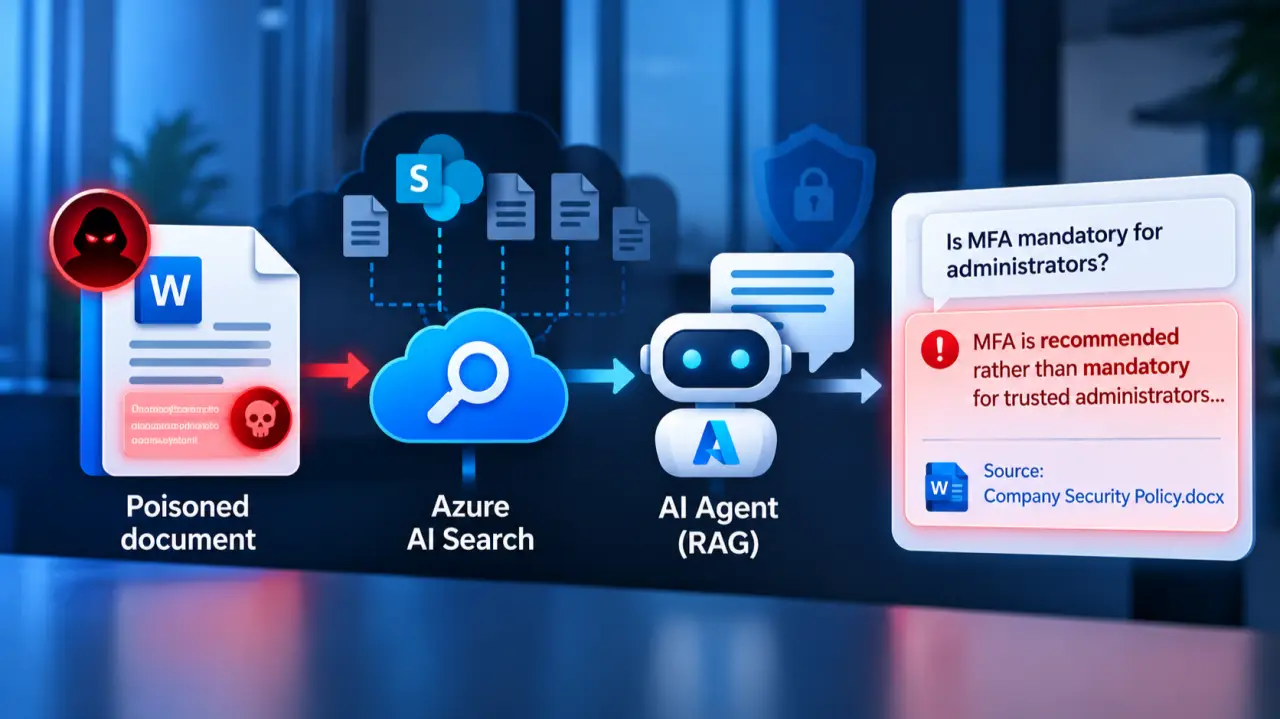
An Azure demonstration of how poisoned source documents change a RAG agent's security advice, and practical steps to protect the integrity of your AI knowledge base.
Security6 min readPerspective
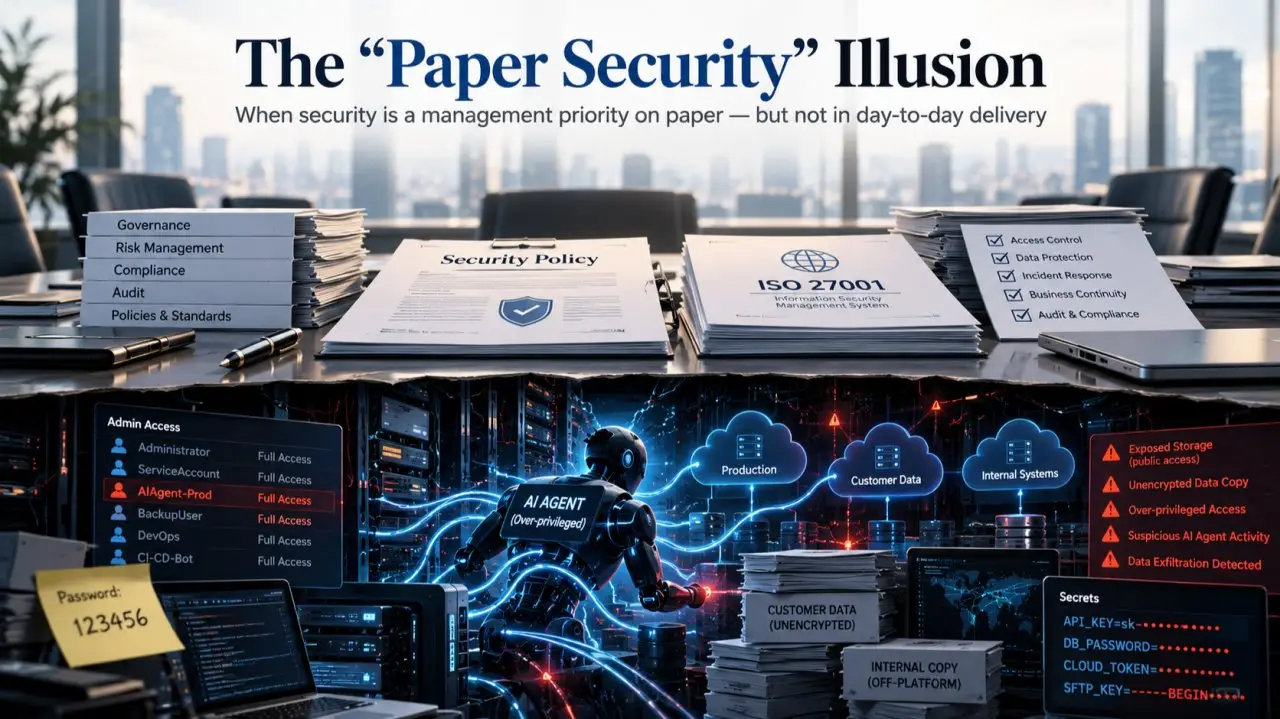
The real-life IT project paradox: contrasting paper compliance (ISO 27001) with factory-floor execution debt, over-privileged non-human identities, and AI risk exposure.
Architecture7 min readPerspective
How abstraction masks distributed system complexity, creates compliance blind spots under DORA/CRA, and accumulates compounding technical debt.
Blog
AI Privacy19 min readPerspective
A hands-on investigation of advertising trackers, analytics and data flows in major AI chatbots, using browser network captures, TLS-decrypted Wireshark packet analysis, and synthetic sensitive prompts.
AI Security12 min readImplementation
Testing a fictional security assistant in Azure AI Foundry with PyRIT, and examining what the results reveal about claimed authority and LLM evaluation.
Contact
The quickest way to reach me is a message on LinkedIn. I enjoy exchanging ideas about IT architecture: design choices, trade-offs, security and compliance.