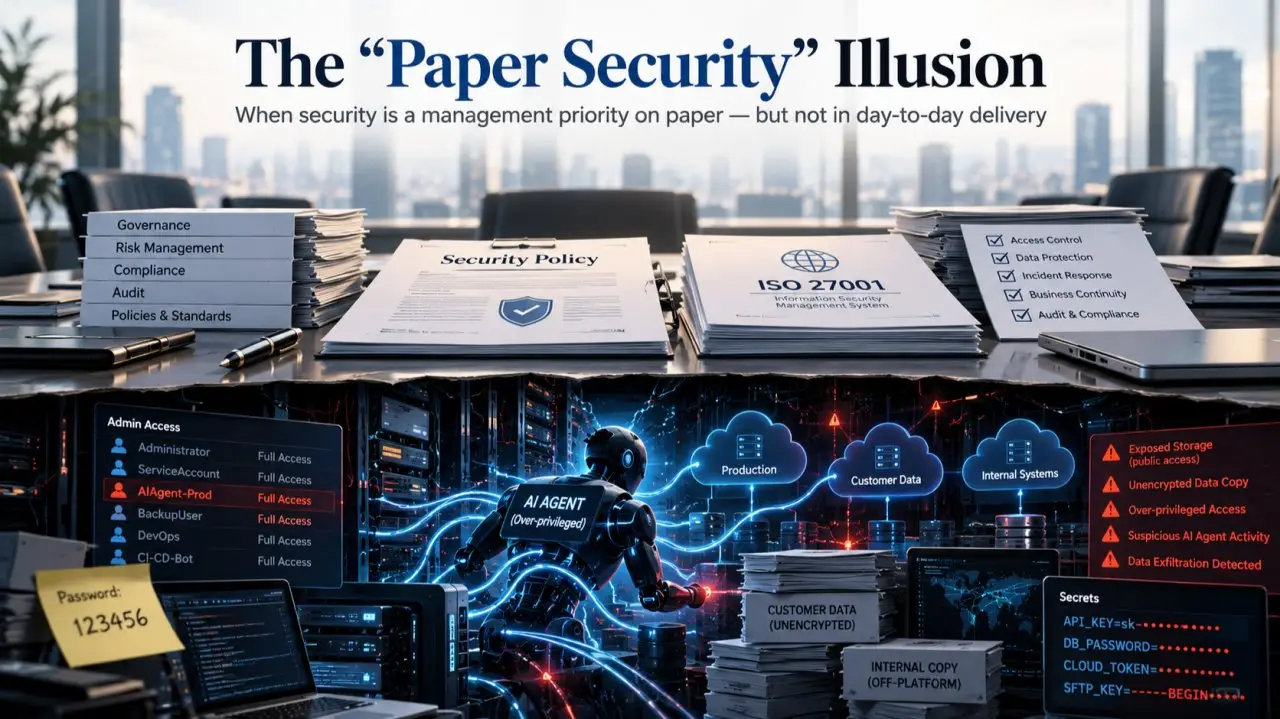
The real-life IT project paradox: contrasting paper compliance (ISO 27001) with factory-floor execution debt, over-privileged non-human identities, and AI risk exposure.
Where Retrieval-Augmented Generation falls short for AI agents, how Andrej Karpathy's LLM Wiki idea synthesizes knowledge once instead of at every query, and the open questions that remain.
Set up Ollama, a local model and the Continue extension for private, offline AI coding assistance in VS Code, no cloud service or massive GPU required.
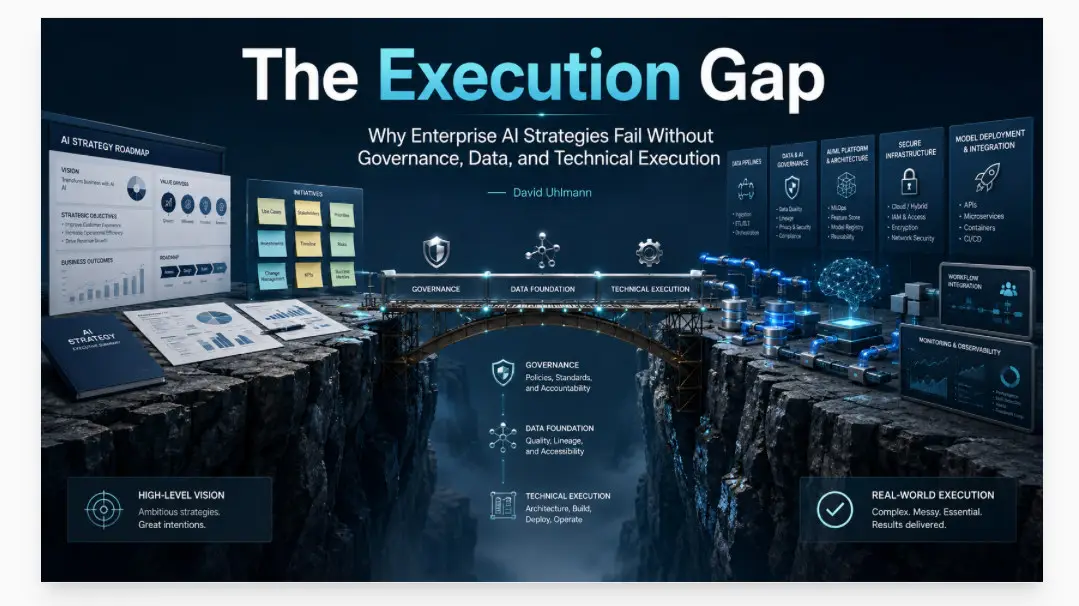
Why so many enterprise AI strategies never reach production, and how pairing strategy with legal constraints, core processes and technical architecture from day one closes the execution gap.
Why processing personal data through internal AI systems needs purpose compatibility, a valid lawful basis under Art. 6 GDPR, and a DPIA under Art. 35 before processing starts.
The Cyber Resilience Act ends the shared responsibility model: secure by default, 24-hour vulnerability reporting and data as damage under the PLD. Concrete steps to prepare now.
How the EU AI Act, GDPR and NIS2 overlap in every IT project, and a unified process for risk management, incident reporting and privacy by design instead of regulatory fear.
Ten recurring risk and compliance pitfalls in IT projects, from production data in test environments to missing SIEM, and what to do instead under NIS2, GDPR and the CRA.
The revised Product Liability Directive explicitly covers software, so defective software can now ground liability claims. What this means for IT projects, with the Dutch implementation as an example.
What qualifies as high-risk AI under Article 6 and Annexes I and III of the EU AI Act, which requirements follow from it, and why skipping the classification can be costly.
An overview of the EU regulations that matter for IT security in 2026 (GDPR, NIS2, CRA, the AI Act and the Product Liability Directive) and why IT implementers can no longer push compliance onto the customer.
Why copying production data into test environments breaks GDPR purpose binding, and how to minimise the risk with automated PII anonymisation using Microsoft Presidio.
A step-by-step walkthrough of building an Azure AI Foundry agent grounded in EU and pharmaceutical regulations via Azure AI Search, to get more precise answers in regulated industries.