Strategy8 min readPerspective
What if the AI hype is misleading and the business model changes?
How open-weight models and private AI infrastructure could reshape enterprise AI economics and create new opportunities for IT consulting.
Strategy8 min readPerspective
How open-weight models and private AI infrastructure could reshape enterprise AI economics and create new opportunities for IT consulting.
Security8 min readImplementation
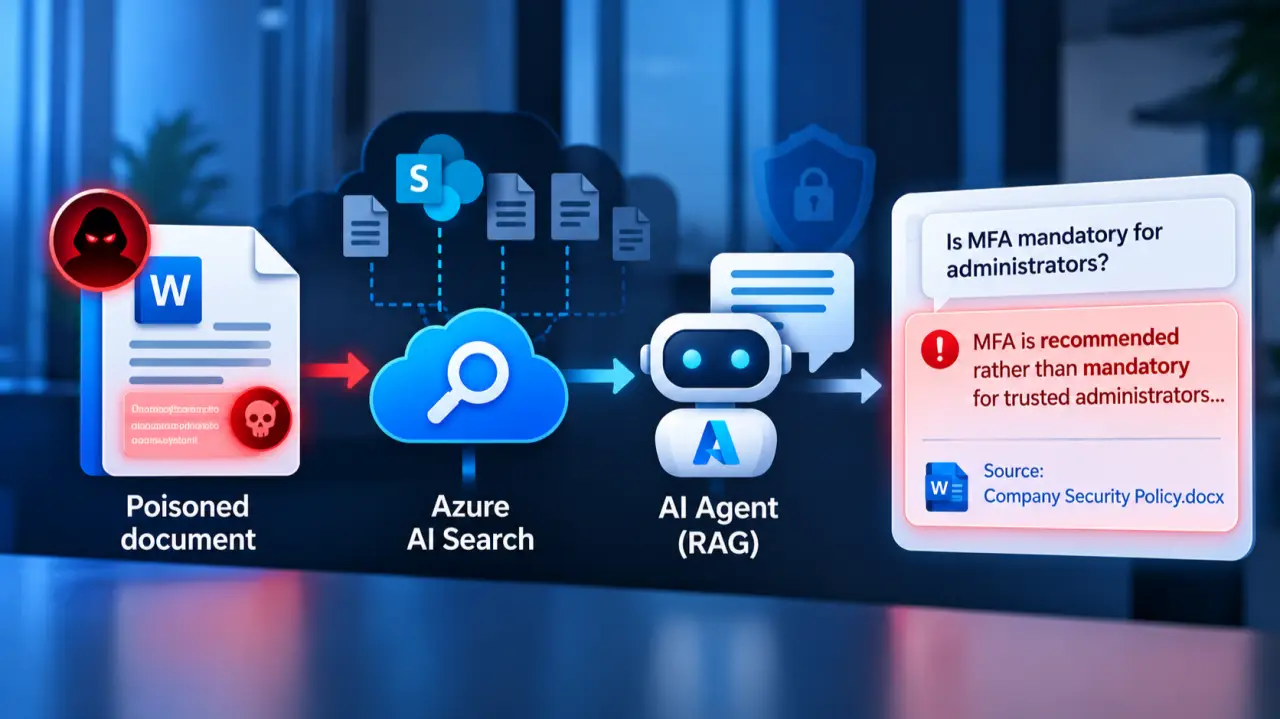
An Azure demonstration of how poisoned source documents change a RAG agent's security advice, and practical steps to protect the integrity of your AI knowledge base.
Security6 min readPerspective
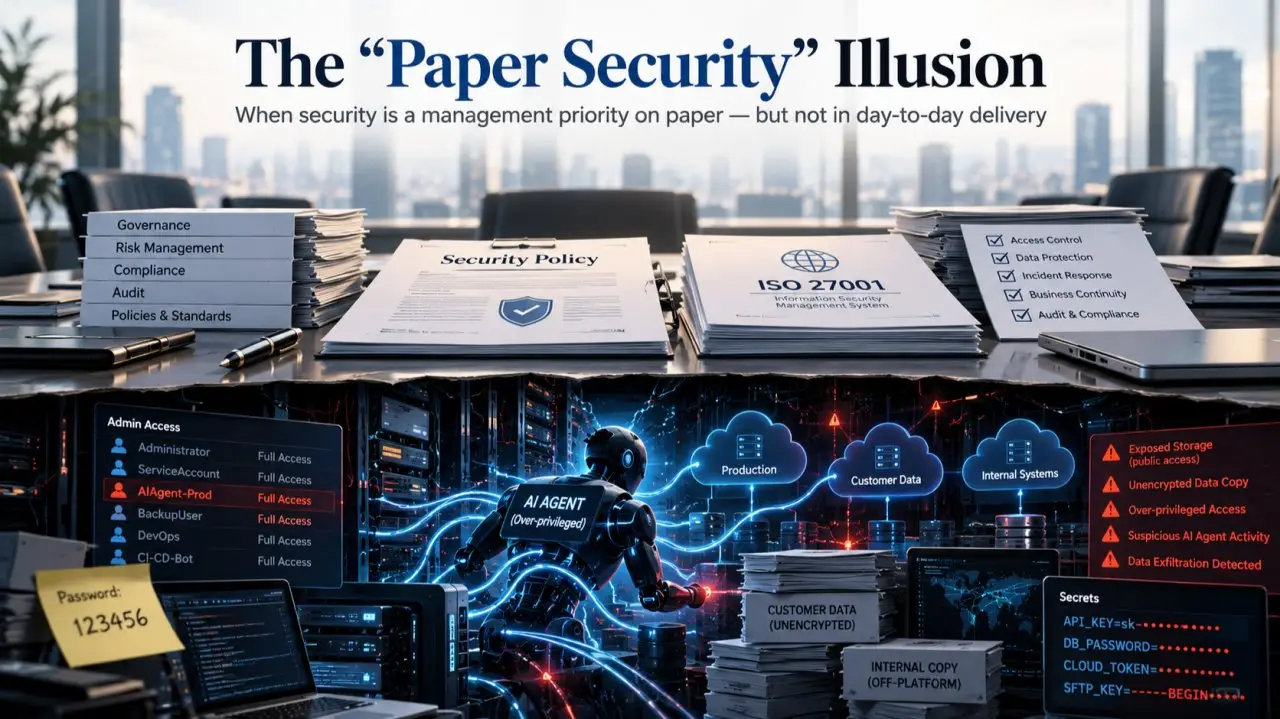
The real-life IT project paradox: contrasting paper compliance (ISO 27001) with factory-floor execution debt, over-privileged non-human identities, and AI risk exposure.
Architecture7 min readPerspective
How abstraction masks distributed system complexity, creates compliance blind spots under DORA/CRA, and accumulates compounding technical debt.
Governance9 min readPerspective
Analyzing psychological distance, cognitive biases, and organizational incentives behind delayed cybersecurity investments under NIS2.
Architecture5 min readPerspective
Where Retrieval-Augmented Generation falls short for AI agents, how Andrej Karpathy's LLM Wiki idea synthesizes knowledge once instead of at every query, and the open questions that remain.
Strategy7 min readPerspective
Why AI success requires strategy, governance, business value and advisory before technical implementation begins.
Strategy5 min readPerspective
Retaining institutional intelligence through decision telemetry logging, manual SOP drills, contractually secured fine-tuning data, and deterministic AI contracts.
Strategy6 min readPerspective
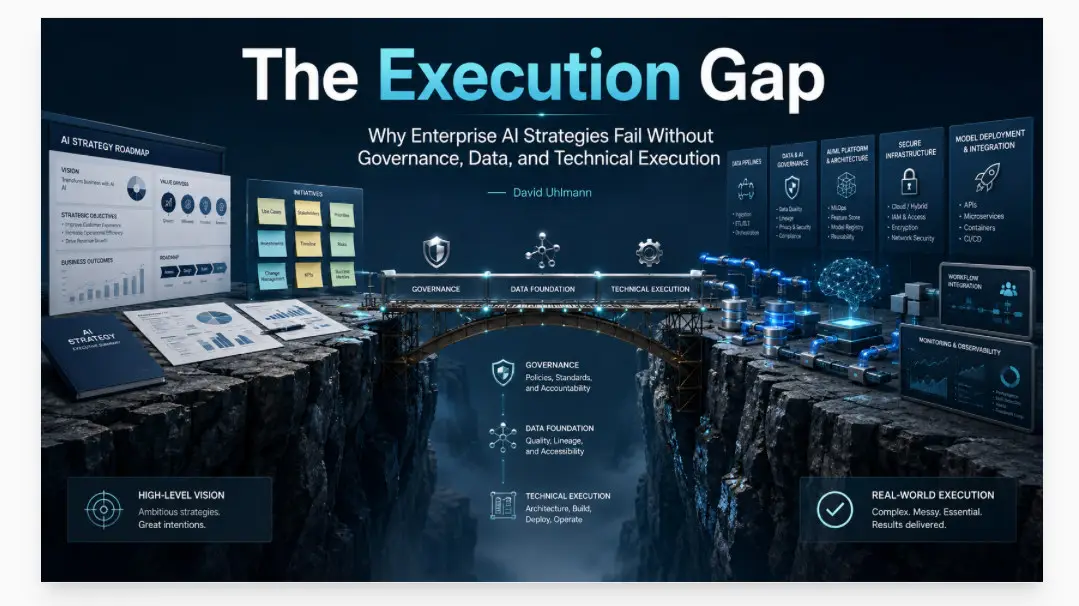
Why so many enterprise AI strategies never reach production, and how pairing strategy with legal constraints, core processes and technical architecture from day one closes the execution gap.
Compliance5 min readRegulatory analysis
Why processing personal data through internal AI systems needs purpose compatibility, a valid lawful basis under Art. 6 GDPR, and a DPIA under Art. 35 before processing starts.
Security5 min readRegulatory analysis
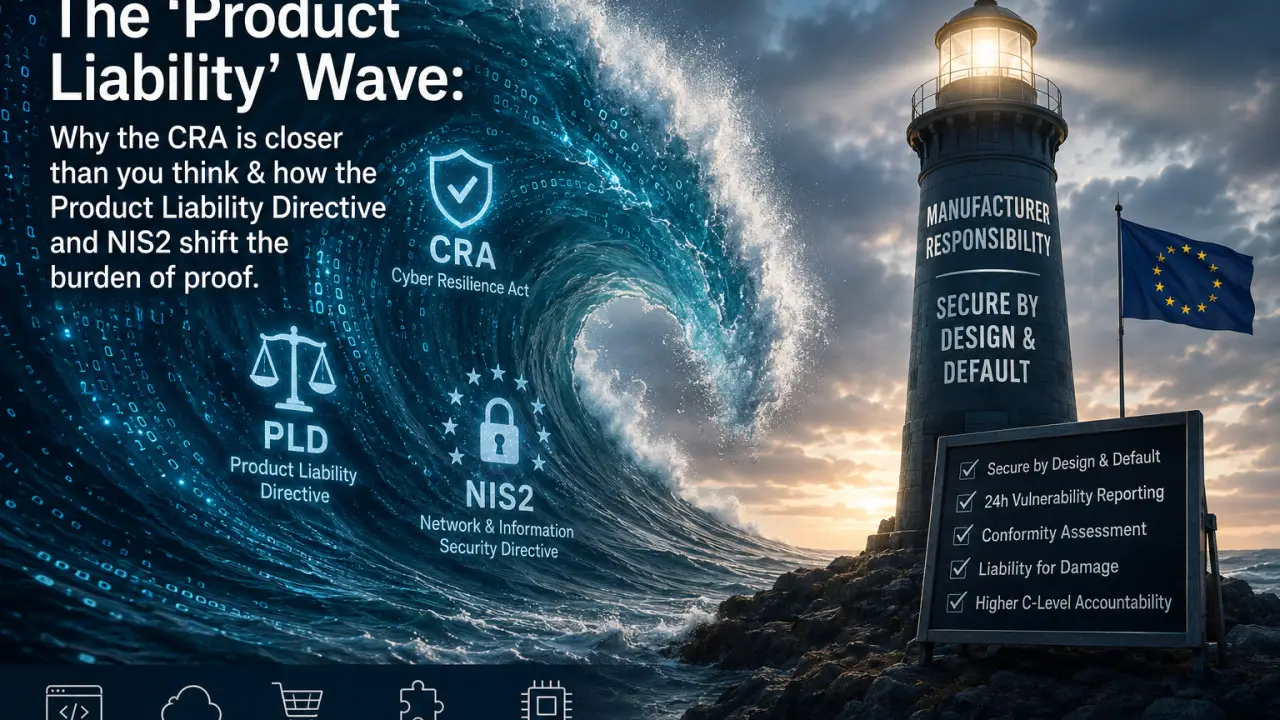
The Cyber Resilience Act ends the shared responsibility model: secure by default, 24-hour vulnerability reporting and data as damage under the PLD. Concrete steps to prepare now.
Compliance16 min readRegulatory analysis
How the EU AI Act, GDPR and NIS2 overlap in every IT project, and a unified process for risk management, incident reporting and privacy by design instead of regulatory fear.
Governance6 min readPerspective
Ten recurring risk and compliance pitfalls in IT projects, from production data in test environments to missing SIEM, and what to do instead under NIS2, GDPR and the CRA.
Compliance4 min readRegulatory analysis
The revised Product Liability Directive explicitly covers software, so defective software can now ground liability claims. What this means for IT projects, with the Dutch implementation as an example.
Compliance10 min readRegulatory analysis
What qualifies as high-risk AI under Article 6 and Annexes I and III of the EU AI Act, which requirements follow from it, and why skipping the classification can be costly.
Security9 min readRegulatory analysis
An overview of the EU regulations that matter for IT security in 2026 (GDPR, NIS2, CRA, the AI Act and the Product Liability Directive) and why IT implementers can no longer push compliance onto the customer.
Compliance6 min readRegulatory analysis
Why copying production data into test environments breaks GDPR purpose binding, and how to minimise the risk with automated PII anonymisation using Microsoft Presidio.
Engineering8 min readImplementation
A step-by-step walkthrough of building an Azure AI Foundry agent grounded in EU and pharmaceutical regulations via Azure AI Search, to get more precise answers in regulated industries.